Data Protection Officer

Outsourced Data Protection Officer DPO service

A registered DPO with regulatory experience, available for a predictable monthly fee and with capacity tailored to your organisation. Expert oversight of GDPR compliance, so you can focus on your business.

Former NAIH expert Legal + cybersecurity expertise Ready to start
Who needs a DPO?
Instant fee estimate DPO service

How much does a DPO service cost?

Adjust the sliders and answer the questions to see your estimated monthly fee.

Core documentation is in place, including processing records, notices and policies, but regular reviews and training are missing.
Do you process special category data, such as health or biometric data?
Number of data subjects (customers, employees and others)
Do you transfer personal data outside the EU?
Has your organisation previously appointed a DPO?
Estimated monthly feeHUF 210,000–250,000Indicative monthly fee · excluding VAT
What does the monthly fee cover?View the full scope
Free consultation Response within 24 hours GDPR compliant

This estimate is indicative. We confirm the monthly fee and scope of service in a tailored proposal following a free initial consultation.

The essentials

What is a Data Protection Officer, and who needs to appoint one?

A Data Protection Officer (DPO) provides independent expert oversight of your organisation’s personal data processing. They advise management and staff, monitor compliance, support impact assessments and data subject requests, coordinate privacy incident response and act as the contact point for Hungary’s data protection authority, NAIH.

GDPR Articles 37–39

GDPR Articles 37–39 govern the DPO’s appointment and duties. The authority must be notified of the appointment and contact details must be made publicly available.

The DPO may be an employee or an external expert engaged under a service agreement; the GDPR expressly permits both arrangements.

When is appointment mandatory?

Under the GDPR, a DPO must be appointed where the organisation:

01

A public authority or body

Local authorities, government-funded bodies, public institutions and public service providers.

02

Core activities involve regular, systematic monitoring of individuals on a large scale

Examples include extensive CCTV, online behavioural tracking and profiling, fleet tracking, telecommunications or credit assessment processing, and direct marketing to a large customer base.

03

Core activities involve large-scale processing of special category or criminal offence data

This may include healthcare providers, private clinics, laboratories, pharmacies, insurers, health funds, occupational health and recruitment companies, and educational or social care institutions.

Hungary’s Information Act may require appointment in additional cases. A voluntarily appointed DPO is subject to the same requirements for independence, expertise and notification as a mandatory appointment.

Does your organisation need a DPO? We can clarify this in a free 30-minute consultation.

Why appoint a DPO even when it is optional?

GDPR obligations apply independently of a DPO appointment. Organisations need appropriate processing records and notices, timely breach notifications where required, and responses to data subject requests. These duties often fall informally to management, HR or IT. An outsourced DPO gives them expert attention within agreed monthly capacity and supports regulatory enquiries and complaints. Many clients choose this voluntarily because privacy matters to the trust of customers, partners and employees.

  • Records of processing activitiesGDPR Article 30
  • Privacy noticesGDPR Articles 13–14
  • Breach notificationwithin 72 hours
  • Responses to data subject requestswithin one month

What is the risk of not appointing a DPO?

Where appointment is mandatory, failing to appoint a DPO can itself attract fines of up to €10 million or 2% of worldwide annual turnover. Breaches of the GDPR’s core principles may attract up to €20 million or 4%. NAIH can also restrict or suspend processing and publish its decisions. In practice, mishandled incidents and unanswered data subject requests can quickly escalate into regulatory complaints.

€10m / 2%
Failure to appoint a DPO where required
€20m / 4%
Breaches of core processing principles

Restrictions and public decisions NAIH may suspend processing as well as impose fines, and publishes its decisions.

Updated: September 2026

Included in your monthly fee

What does our monthly DPO service cover?

A named zemITis expert becomes your registered DPO, identified on your website and in your privacy notices. The monthly fee typically includes 8–20 dedicated expert hours, depending on size, processing activities and maturity. Your proposal specifies the agreed capacity and covers the following work:

01

Records and documentation

  • Records of processing activities: creating and maintaining the register, and identifying processing activities not yet recorded (GDPR Article 30).
  • Privacy policies and notices: developing or reviewing internal privacy and data security policies, and notices for employees, customers, CCTV, websites and cookies.
  • Data processing and joint controller agreements: reviewing existing agreements, drafting missing arrangements and checking supplier privacy compliance (GDPR Article 28).
  • Lawful bases and retention periods: reviewing legal grounds, legitimate interests assessments, consent management and international transfer compliance.
02

Risk management and planning

  • Data Protection Impact Assessments (DPIAs): assessing the need for a DPIA and coordinating and documenting assessments for new systems, CCTV, HR tools or AI solutions.
  • Data protection by design and by default: advice when designing new processes, IT systems, marketing initiatives and HR solutions.
  • Annual privacy review: a yearly compliance assessment and prioritised action plan.
03

Data subject rights and breaches

  • Data subject requests: expert handling of access, erasure, rectification, objection and portability requests, with coordination of responses within the applicable deadlines.
  • Personal data breaches: establishing response procedures, assessing breaches, preparing notifications to NAIH within 72 hours where required, preparing communications to affected individuals and maintaining the breach register.
04

Regulatory liaison and awareness

  • Liaison with NAIH: DPO registration, expert support for enquiries, investigations and complaints, and preparation of submissions.
  • One general and one targeted privacy training session each year for teams such as HR, customer service, marketing or management, plus awareness material for new starters.
05

Reporting and advice

  • Quarterly management reporting on compliance status, open actions, incidents and requests, together with an annual DPO report.
  • Ongoing expert advice on day-to-day privacy matters by email and phone, within agreed response times.

A named expert, backed by a team

Your registered DPO is a named expert supported by information security and compliance colleagues. Documents undergo independent peer review before delivery. This provides broader expertise and continuity, reducing reliance on a single person while regulatory deadlines continue to apply.

  1. Ongoing support Requests, breaches and advice
  2. Quarterly Management report
  3. Annually Annual review, two training sessions and updated records
Compare your options

In-house or outsourced DPO? Independence, conflicts and availability

The DPO acts independently, receives no instructions about how to carry out their statutory duties and reports directly to senior management. They must not determine the purposes and means of the processing they oversee, which commonly creates conflicts for managing directors and heads of IT, HR or marketing. Identifying, training and safeguarding the independence of a suitable internal person can be a significant burden for a role requiring only a few hours a month.

Szempont In-house DPO (employee) zemITis kiszervezett DPO
Independence and conflicts of interest Decision-making roles may conflict with DPO duties; the organisation must demonstrate competence and independence An external, independent specialist with a clearly defined role
Professional expertise Typically a legal or IT background supplemented by self-directed learning A lawyer and cybersecurity law specialist with five years of regulatory experience, backed by information security experts
Getting started Selection, training and employment arrangements can take months Ready to start after signing; we prepare the NAIH notification
Availability No built-in cover for leave, illness or resignation, while breach and request deadlines continue to apply A team supports the registered DPO, ensuring continuity
Protection of the DPO role A DPO cannot be dismissed or penalised for performing their duties, which must be reflected in internal employment arrangements A service agreement with a clear scope and termination terms
Regulatory liaison A learning curve during the first investigation Established familiarity with regulatory procedures from inside the authority
Cost Salary and employer contributions for a part-time responsibility, plus ongoing training A predictable monthly fee aligned with actual needs
Objectivity Internal relationships and pressure from colleagues An external, evidence-based perspective informed by regulatory experience

An outsourced DPO provides the independence, expertise and ongoing availability the role requires, without hiring a full-time privacy lawyer.

Why zemITis

Why choose zemITis for your DPO?

A regulator’s perspective

Our DPO spent five years at Hungary’s National Authority for Data Protection and Freedom of Information (NAIH), gaining first-hand insight into how the authority conducts its investigations.

Legal and cybersecurity expertise

Today’s privacy questions span law, technology and information security. Our service brings these perspectives together.

A named expert, backed by a team

Privacy, information security and compliance experts support your registered DPO. Every document undergoes independent peer review before delivery.

Business focus

We design workable processing arrangements that meet privacy requirements and support your business.
Your expert

Who will be your organisation’s registered Data Protection Officer?

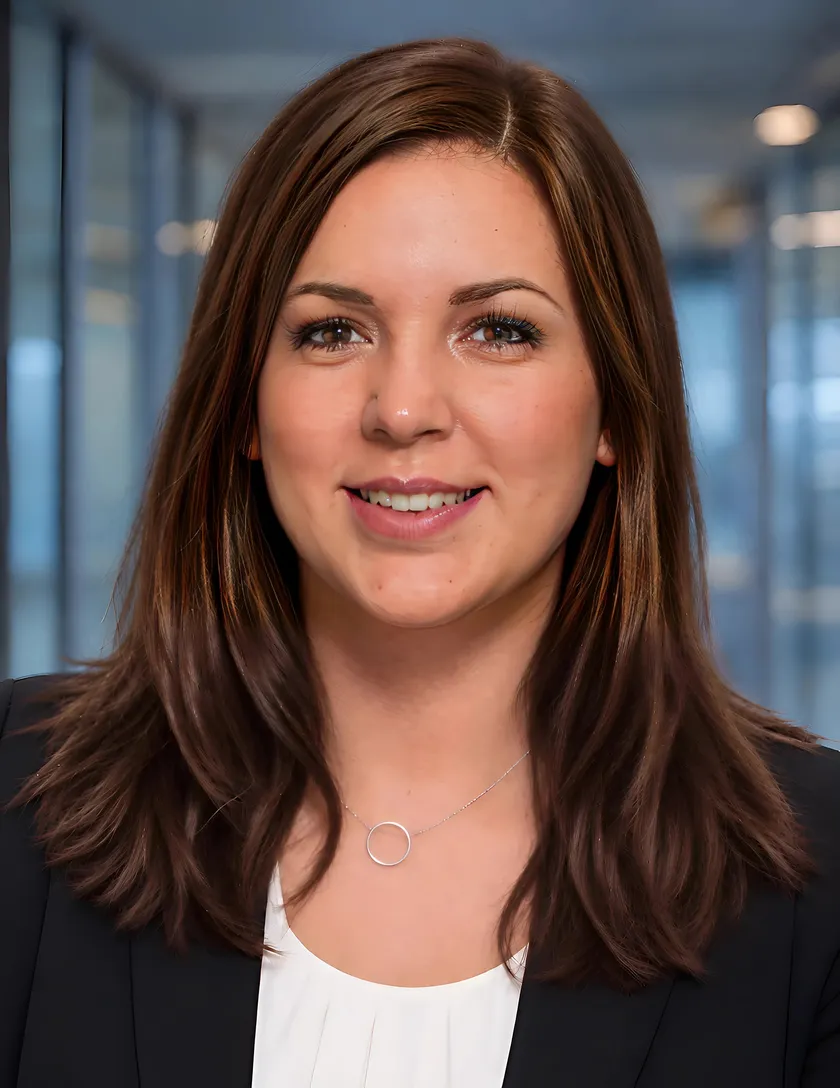
Dr Fanni Mikoss, Data Protection Officer, lawyer and cybersecurity law specialist
Lawyer Cybersecurity law specialist

Dr Fanni Mikoss

Lawyer and cybersecurity law specialist; privacy and information security adviser, former NAIH expert

Fanni graduated cum laude in law from Pázmány Péter Catholic University, then completed postgraduate studies in cybersecurity law at Széchenyi István University. She spent five years as a data protection expert at NAIH, conducting compliance investigations, assessing requests and complaints, preparing regulatory decisions, cooperating with EU authorities on cross-border cases and developing expert opinions. She understands the evidence regulators expect and where organisations encounter difficulties.

As an adviser and DPO for corporate clients, she develops privacy and information security policies, records and notices, conducts compliance reviews and internal audits, and reviews contracts. She also contributes to NIS2, ISO 27001 and AI Act projects and regularly delivers privacy and security training to employees and management.

Regulatory focus
GDPRHungarian Information ActNIS2ISO/IEC 27001DORAAI Act
Tapasztalat
Regulatory investigations and decision preparationDPO service deliveryPrivacy and information security auditsPolicy framework developmentTraining
Nyelvek
Magyar (anyanyelv)Angol (C1)German (B2) Support for international groups and cross-border processing.

“At the authority, I learned that many fines stem from oversights: an unanswered request, a late breach notification or a missing processor agreement. As a DPO, my role is to help prevent these issues and, if they do arise, ensure the organisation is prepared to respond to the authority.”

Dr Fanni Mikoss
Our process

How do we get started?

1
Step 01 30 minutes

Free consultation

We assess whether you need a DPO, review your processing activities, any previous regulatory enquiries or breaches, and your current compliance position.

2
Step 02 within 24 hours

Scope and proposal

We agree monthly capacity, responsibilities and response times, then provide a tailored fixed-fee proposal.

3
Step 03

Contract, appointment and NAIH notification

We prepare the appointment document, NAIH notification and the wording for your website and privacy notices, ready for your approval and signature.

4
Step 04 first 30 days

Privacy assessment

We review your processing records, notices, data processing agreements, breach response and request handling, then provide a prioritised action plan.

5
Step 05

Ongoing delivery

Support for requests, breaches and everyday questions, quarterly management reports, annual reviews and training, with prompt expert assistance for regulatory enquiries.

Facing an investigation or a recent breach? We will align the assessment and start of our work with your deadline.
Book a consultation

Your information is secure with us

As privacy advisers, we apply the same principles to our own work that we recommend to clients.

  • Least-privilege access Access to systems containing personal data is documented and restricted to what our work requires, typically on a read-only basis.
  • Segregated storage We manage and store each client’s documentation separately in a controlled Microsoft 365 Business Premium environment with enhanced security settings.
  • Four-eyes review Every document is independently reviewed by another expert before delivery.
  • Confidentiality and data processing We work under a non-disclosure agreement and, where the activities require it, a data processing agreement.
FAQ

Common questions about outsourced DPO services

Appointment is required for public authorities or bodies, and where core activities involve large-scale regular and systematic monitoring, or large-scale processing of special category or criminal offence data. Otherwise, appointment may be voluntary, while other GDPR obligations still apply. We can clarify your position in a free 30-minute consultation.
Yes. The GDPR expressly allows a DPO to perform their duties under a service contract. The external DPO must be notified to NAIH and their contact details published, just as for an internal appointment. A named zemITis expert will be your registered DPO.
This is generally unsuitable and often incompatible with the role. A DPO must not hold a position in which they determine the purposes and means of processing. Conflicts commonly arise in executive, IT, HR and marketing leadership roles. Independence is a key regulatory consideration and a common reason to outsource.
A DPO independently oversees personal data processing under the GDPR, with NAIH as the supervisory authority. The Information Security Officer (IBF) oversees electronic information system security under Hungary’s Cybersecurity Act; for commercial entities, SZTFH is the supervisor. The roles complement one another and need to work closely together, as an incident may require notification under both regimes. Our outsourced security officer service
Your organisation makes the appointment. The authority must be notified of the DPO’s name and contact details, and contact information must be published, typically on your website and in privacy notices. We prepare the notification and publication wording for your approval.
The DPO responds within the agreed timeframe, assesses the risk and prepares any required notification to NAIH within 72 hours. Where the breach poses a high risk to individuals, we also prepare communications to them. We maintain the breach register; your IT team or provider handles technical remediation, coordinated and documented with DPO support.
Immediately after the contract is signed. We prepare the appointment and NAIH notification in the first few days. The privacy assessment and action plan are typically completed within 30 days.
The service supports ongoing compliance, so we typically agree an initial 12-month term followed by an open-ended contract. Your proposal sets out the exact terms.
Yes. The GDPR allows a group to appoint one DPO if they are easily accessible from each establishment. Appointment and notification arrangements must still cover the relevant companies. We manage these and tailor capacity to the group’s size.
A controller’s responsibility under the GDPR cannot be transferred. Your organisation and management remain accountable for lawful processing, while the DPO advises, monitors and liaises with the authority. zemITis accepts contractual responsibility for professional delivery of the assigned duties and supports management with regular reports and advice.
Documentation is the starting point. Regulatory investigations examine how procedures work in practice: maintained records, timely responses, breach notifications and supplier agreements. A DPO provides ongoing oversight and reviews your existing documentation during the first 30 days.
Yes. AI solutions can process personal data through profiling or automated decision-making, potentially requiring DPIAs and additional transparency under the GDPR. The AI Act introduces further transparency and risk management requirements. Our expert understands both frameworks, and the service can be linked to an ISO/IEC 42001 AI management project. ISO/IEC 42001 (AI management)
Get started

A DPO with regulatory experience, without a full-time legal hire.

A free 30-minute consultation and a tailored proposal within 24 hours.