

Many organisations already have IT staff, an external operations provider and security tools. Yet it may still be unclear who coordinates risk management, follows up security actions or owns the incident reporting process.
We refer to this role as the Information Security Officer, or IBF in Hungarian. The precise statutory term is the person responsible for the security of the electronic information system. This guide explains who needs an appointment and how to turn the role into an effective service.
Why must an officer be appointed?
Section 11 of Act LXIX of 2024 requires management to appoint an internal person or reach an agreement with an external expert. The purpose is to ensure delivery of information system protection, the risk management framework, incident reporting and liaison with the incident response centre.
An appointment therefore needs more than a name in a register. It requires authority, information, resources and regular access to management. IT operations keeps systems running; the security officer ensures security requirements and risks are reflected in operations and decisions in a traceable way.
Who needs an Information Security Officer in Hungary?
The starting point is the scope of Hungary’s Cybersecurity Act. Businesses must assess sector and size together. Some entities are covered regardless of size or through a specific regulatory designation.
Sector and activity
Annexes 2 and 3 include energy, transport, healthcare, water utilities, digital infrastructure and certain ICT providers, as well as specified manufacturing, food and other activities.
A broad sector label is not sufficient. Match actual operations to the specific activities and entity types in the annexes. Financial organisations must separately assess the interaction between DORA and Hungarian cybersecurity requirements.
Size: more than the 50-employee threshold
Section 1(1)(d) identifies medium-sized enterprises and organisations in the listed sectors meeting either of these conditions:
- at least 50 employees;
- annual net turnover or budgeted revenue exceeds €10 million, and, for entities required to prepare financial statements, the balance sheet total also exceeds €10 million.
The “and” in the financial test matters: turnover alone does not describe this alternative. SME classification also requires consideration of partner and linked enterprises.
Exceptions and obligations regardless of size
Size is not a general exemption for certain electronic communications, trust, DNS, top-level domain registry and domain registration providers. Separate rules cover public administration, specified state and defence bodies, and entities designated by an authority.
Being a supplier does not automatically place a business within statutory scope. A customer may impose contractual security requirements or require a responsible contact even when the supplier is not independently covered. Assess obligations arising from the supplier’s own activities or regulatory designation separately.
Which authority is responsible?
Cybersecurity supervision and incident response are different functions. Entities outside public administration falling under Section 1(1)(d) and (e) are generally supervised by SZTFH. Other groups may fall under the national or defence cybersecurity authority.
It is therefore incorrect to direct every appointment to the same authority. Match registration, change notifications and incident reporting channels to your own classification. SZTFH’s supervision guidance is a useful starting point for businesses in its remit.
What does the officer do in practice?
These are typical activities and deliverables. The exact scope depends on your systems, obligations and engagement.
| Activity | Tangible output |
|---|---|
| Policies and responsibilities | Current policies and approved allocation of duties |
| System inventory and classification support | A clear system register and documented classifications |
| Risk management | Risk register and action plan with owners and deadlines |
| Incident management | Known reporting channels, contacts and practicable scenarios |
| Awareness and training | Role-specific training and measurement |
| Audit preparation | Organised evidence and tracked corrective actions |
| Management reporting | Decision-ready information on residual risks |
If the starting position is unclear, a gap analysis identifies gaps and priorities. Our separate article explains incident reporting deadlines and responsibilities.
Who can hold the role? Can it be the IT lead?
Assess eligibility under Section 11 and the applicable implementing rules. Legal capacity and a clean criminal record are baseline requirements. Education, qualifications and experience requirements may differ by entity type; an international certification is not automatically a statutory exemption.
It is also inaccurate to say that an IT lead is always excluded. Section 11(4) prohibits specified combinations with operations, development and financial management duties, but subsection (5) contains exceptions, including for entities under Section 1(1)(d) and (e).
Beyond legal eligibility, consider whether control oversight receives enough attention and whether difficult but necessary security findings reach management.
When is outsourcing a good choice?
An external model can suit organisations that need continuous expertise, audit experience and predictable delivery. Define the named officer, cover arrangements, response times, management meetings and required deliverables in the contract.
Outsourcing organises delivery; the organisation and management retain their legal responsibilities. An internal contact and cooperation from the IT team remain essential.
Our in-house versus outsourced comparison explores the decision in more detail. See our security officer service for the practical scope and team behind it.
Five mistakes to avoid
- A nominal appointment: the officer receives no access, information or opportunity to support decisions.
- An incomplete scope assessment: only headcount is checked, overlooking activities and special rules.
- Unclear responsibilities: operations, management and the officer each wait for someone else during an incident.
- Retrospective evidence: control performance is not recorded, making it difficult to demonstrate at audit.
- Confusing appointment with audit readiness: a service agreement alone does not resolve technical and organisational gaps.
SZTFH’s guidance states that the first audit deadline for affected organisations operating before 1 January 2025 was 30 June 2026. Newly covered organisations have different deadlines linked to registration. A new officer engagement does not reset an expired deadline; outstanding gaps and next steps must be addressed separately.
How does the engagement begin?
We first establish scope, systems and existing documentation. This informs the appointment, access arrangements, initial assessment and management-approved action plan. Regular reporting, tracked actions and reviews then support ongoing decisions.
Our outsourced service can support both NIS2 preparation and longer-term security operations. Get a security officer fee estimate, and we will discuss the right model for your organisation.
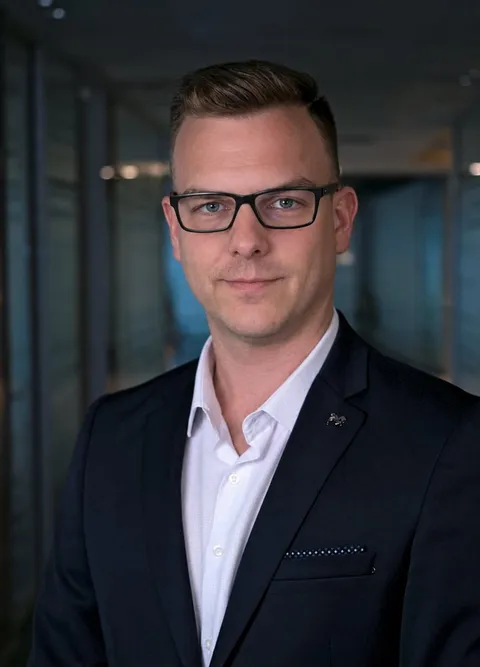
Dávid Meisitz
Senior IT Compliance and NIS2 Readiness Expert · CISA, CISM, ISO/IEC 27001 Lead Auditor
Dávid has over ten years of experience in IT compliance and risk management, having started his career in Deloitte’s IT audit and security team. As the registered Information Security Officer for several organisations, he brings together risk management, executive decision-making and audit preparation.
Once you know the requirements, Dávid and the zemITis team help you set implementation priorities. Discover how we turn a formal appointment into clear responsibilities, trackable actions and regular management reporting.
Frequently asked questions
Can the security officer role be outsourced?
Yes. Section 11 of Hungary’s Cybersecurity Act permits an internal appointment or an agreement with an external person. The individual performing the work, their authority and working arrangements must be clearly defined.
Can the IT lead also be the security officer?
This depends on the organisation’s legal classification. Section 11(4) sets conflict rules, but subsection (5) includes exceptions, including entities under Section 1(1)(d) and (e). Check actual duties and whether an exception applies.
Does a DPO replace the security officer?
No. A DPO advises on and monitors personal data compliance; an Information Security Officer coordinates information system security. They have different responsibilities.
Does one appointment cover an entire group?
The requirement and appointment must be addressed for each legal entity in scope. A shared expert may be possible where competence, capacity and cooperation requirements are met for every entity.